Home › Legal › Record of Processing Activities
Record of Processing Activities · Public Summary
Every processing activity, on one page.
We maintain a Record of Processing Activities (“RoPA”) under the Digital Personal Data Protection Act, 2023 (“DPDPA 2023”). This page is the public summary for transparency: it tells every Data Principal and every reviewer what the DigiSurvey platform does with personal data, under what legal basis, and with what safeguards.
The detailed internal register — with per-table field inventories, specific sub-processor engagement dates, and operational metadata — is maintained internally and produced to the Data Protection Board of India on inquiry under DPDPA 2023 s.33 and s.36.
1. Processing activities
Columns: Activity · Legal basis under DPDPA 2023 · Data categories · Recipients · Retention · Safeguards.
| Activity | Legal basis | Data categories | Recipients | Retention | Safeguards |
|---|---|---|---|---|---|
| Surveyor account management | Contract / Consent | Identity (name, DoB), contact (email, phone), professional (IRDAI licence no., firm, SLA number) | None (internal) | Until account closure + 1 year | Encryption at rest and in transit; MFA; role-based access |
| Insurer account management | Contract | Identity, contact, authorised users, tenant configuration | None | Until contract end + 1 year | Encryption; MFA; RBAC; tenant isolation |
| Claim / survey processing | Contract / Legitimate interest — necessary for the specified purpose under DPDPA 2023 s.7(c) | Insured identity & contact, vehicle (reg no., chassis, engine, make/model), incident details, photos, videos, OCR-extracted text | The insurer client who commissioned the survey | 7 years from claim settlement (IRDAI Surveyors Reg. 2015 reg. 13; Companies Act books) | Encryption; tenant isolation; row-level security (RLS); audit-logged access |
| OCR processing | Contract / Legitimate interest | Document images (RC, driving licence, insurance papers), extracted text | Google Gemini (sub-processor; India / US datacenters) | Transient at Gemini (not retained per the Google DPA); extracted text stored under the parent claim per Claim/Survey Processing retention above | TLS 1.3; project-scoped API keys; no training on our content (per Google DPA) |
| Billing & payments | Contract / Legal obligation (GST, Companies Act) | Invoice data, GSTIN, Razorpay customer token, payment method token (not card PAN) | Razorpay (payment gateway); statutory recipients (GST, Income Tax) | 8 years (Companies Act 2013 s. 128; CGST Act 2017 s. 36) | Encryption; no PAN or card number stored on our systems; PCI-DSS Level 1 gateway |
| Marketing emails (consent-based only) | Consent — opt-in required and recorded | Email, name, consent timestamp & source | Zoho Campaigns (marketing email sub-processor) | Until unsubscribe; consent-withdrawal record retained for 1 year | Double opt-in confirmation; one-click unsubscribe in every email; separate consent register |
| Transactional emails (bills, OTP, notifications) | Contract (necessary for providing the service) | Email, name, message body | Resend (transactional email sub-processor) | Delivery logs 30 days; message content not retained by Resend beyond send | TLS; DKIM/SPF/DMARC; sending domain under our control |
| Support tickets | Legitimate interest — service delivery and quality | Identity, email, ticket content, attachments | None (internal) | 3 years from ticket close | Encryption; role-based access; redaction of PII in internal review |
| Compliance filings | Legal obligation under DPDPA 2023 s.7(b) | The minimum data necessary for the specific regulator (claim counts, breach particulars, surveyor-firm records) | IRDAI; Data Protection Board of India; CERT-In; GST; Income Tax | As per each regulation (CERT-In 180-day log retention; IRDAI 7 years; GST 6–8 years; IT Act as applicable) | Encrypted archive; access limited to the compliance officers and the Director (Mrs. Monika Sharma) |
| Security logging | Legal obligation (CERT-In Directions 2022) / Legitimate interest | IP, user-agent, authentication events, administrative actions | None (internal) | 18 months rolling (application logs); 180 days (CERT-In mandatory log retention) | Encryption; append-only; separate access role; NIC NTP time-sync |
| Grievance handling | Legal obligation under DPDPA 2023 s.10(2)(d) | Grievance text, Data Principal identity & contact, resolution action | Grievance Officer; where escalated: the Data Protection Board of India | 3 years from closure (statutory limitation period), then anonymised metrics only | Encrypted at rest; access limited to the Grievance Officer and the Directors |
2. International transfers
Primary data (database and media storage) stays in India. The following sub-processors involve a transfer outside India for the purposes stated. The current, complete list is published at /legal/subprocessors, with 14 days’ advance notice before any addition.
| Sub-processor | Role | Region | Transfer basis |
|---|---|---|---|
| Supabase | Database, auth, storage (primary data home) | India (ap-south-1, Mumbai) | No cross-border transfer for primary data; corporate parent US-based (DPA on file) |
| Cloudflare | CDN, WAF, DDoS, Workers (edge compute) | Global edge; TLS termination may be in India PoP; management plane US | Standard Contractual Clauses in Cloudflare DPA; India government-approved cross-border mechanism |
| Cloudflare R2 | Hot-tier object storage for edge-cached media | Global object store with APAC + India POP delivery | Cloudflare R2 DPA; SCCs; India government-approved cross-border mechanism |
| AWS S3 Mumbai (ap-south-1) | Encrypted archival storage, tier 2 (India-resident copy for IRDAI 7-year audit tail) | India (ap-south-1, Mumbai) | No cross-border transfer; AWS DPA on file |
| Google Gemini | OCR, transient only | India / US datacenters | Google DPA; no retention; no training; transfer limited to document images for the duration of the call |
| Razorpay | Payment gateway | India | No cross-border transfer |
| Resend | Transactional email | EU / US | Resend DPA with SCCs; transfer is email metadata only |
| Zoho | CRM, marketing campaigns, workspace | India datacenter preferred; some processing in US | Zoho DPA; India data-residency selected where available |
| Backblaze B2 | Backblaze B2 — ciphertext stored in eu-central and us-west dual-region; decryption passphrase held only by Digitaliiisla, so Backblaze cannot read content. | eu-central & us-west dual-region (ciphertext only) | GPG-encrypted backups only; the passphrase is held by Digitaliiisla; Backblaze cannot read the content |
DPDPA 2023 permits transfer of personal data outside India to any country other than those specifically notified by the Central Government as restricted (DPDPA 2023 s.16). We monitor the restricted list and will update sub-processor routing to comply.
3. Data Subject (Data Principal) rights SOP
Every Data Principal has rights under DPDPA 2023 Chapter III. We handle these at grievance@digitaliiisla.co.in under the Grievance Officer. The Privacy Policy is the authoritative description; this is the operational summary.
- Right of access (s.11). We send a complete export within 30 days of a verified request, in a commonly used machine-readable format (JSON / CSV).
- Right to correction and erasure (s.12). Corrections applied within 7 business days; erasure applied within 30 days, except for data we are legally required to keep (IRDAI 7-year retention for claims; Companies Act books). In those cases we tell the Data Principal exactly what we are keeping, why, and when it will be deleted.
- Right to withdraw consent (s.6(4)). Withdrawal is one-click from marketing emails and immediate from the account settings. Where consent was the sole legal basis, we stop processing on withdrawal.
- Right of grievance redressal (s.13). The Grievance Officer acknowledges within 72 hours and resolves substantively within 30 days.
- Right to nominate (s.14). A Data Principal may nominate another individual to exercise their rights in the event of death or incapacity. We accept nominations in writing through the account settings or by email to the Grievance Officer.
- Verification. We verify requester identity through the account login where possible; where not possible (third-party request, non-account-holder), we ask for a government-issued ID (which we delete after verification unless the law requires us to keep it).
4. Where the detailed RoPA is
- Owner. The Grievance Officer, Mr. Alok Sharma, is the custodian of the detailed internal RoPA, in coordination with the Directors.
- Format. Spreadsheet + per-activity data-flow diagram; stored encrypted; access limited.
- Who sees it. The Data Protection Board of India on inquiry under DPDPA 2023 s.33 / s.36; our statutory auditor on request; insurer customers under NDA when it is relevant to the specific audit scope under Audit Readiness Clause 2.
- Review. Semi-annually, and whenever a new activity, sub-processor, or data category is introduced.
5. Changes to this summary
We may add, remove, or amend activities. Material changes are reflected on this page with a dated revision and announced in our next cycle of the home-page Public Governance Notices. The “Last updated” stamp on the signed block below is authoritative.
Digitaliiisla Technologies Private Limited confirms that the activities, legal bases, data categories, recipients, retention periods, and safeguards described above represent the DigiSurvey platform’s processing of personal data as of the date below. We maintain a detailed internal RoPA from which this summary is derived; we will produce the detailed register to the Data Protection Board of India on inquiry; and we will update this public summary promptly on any material change.
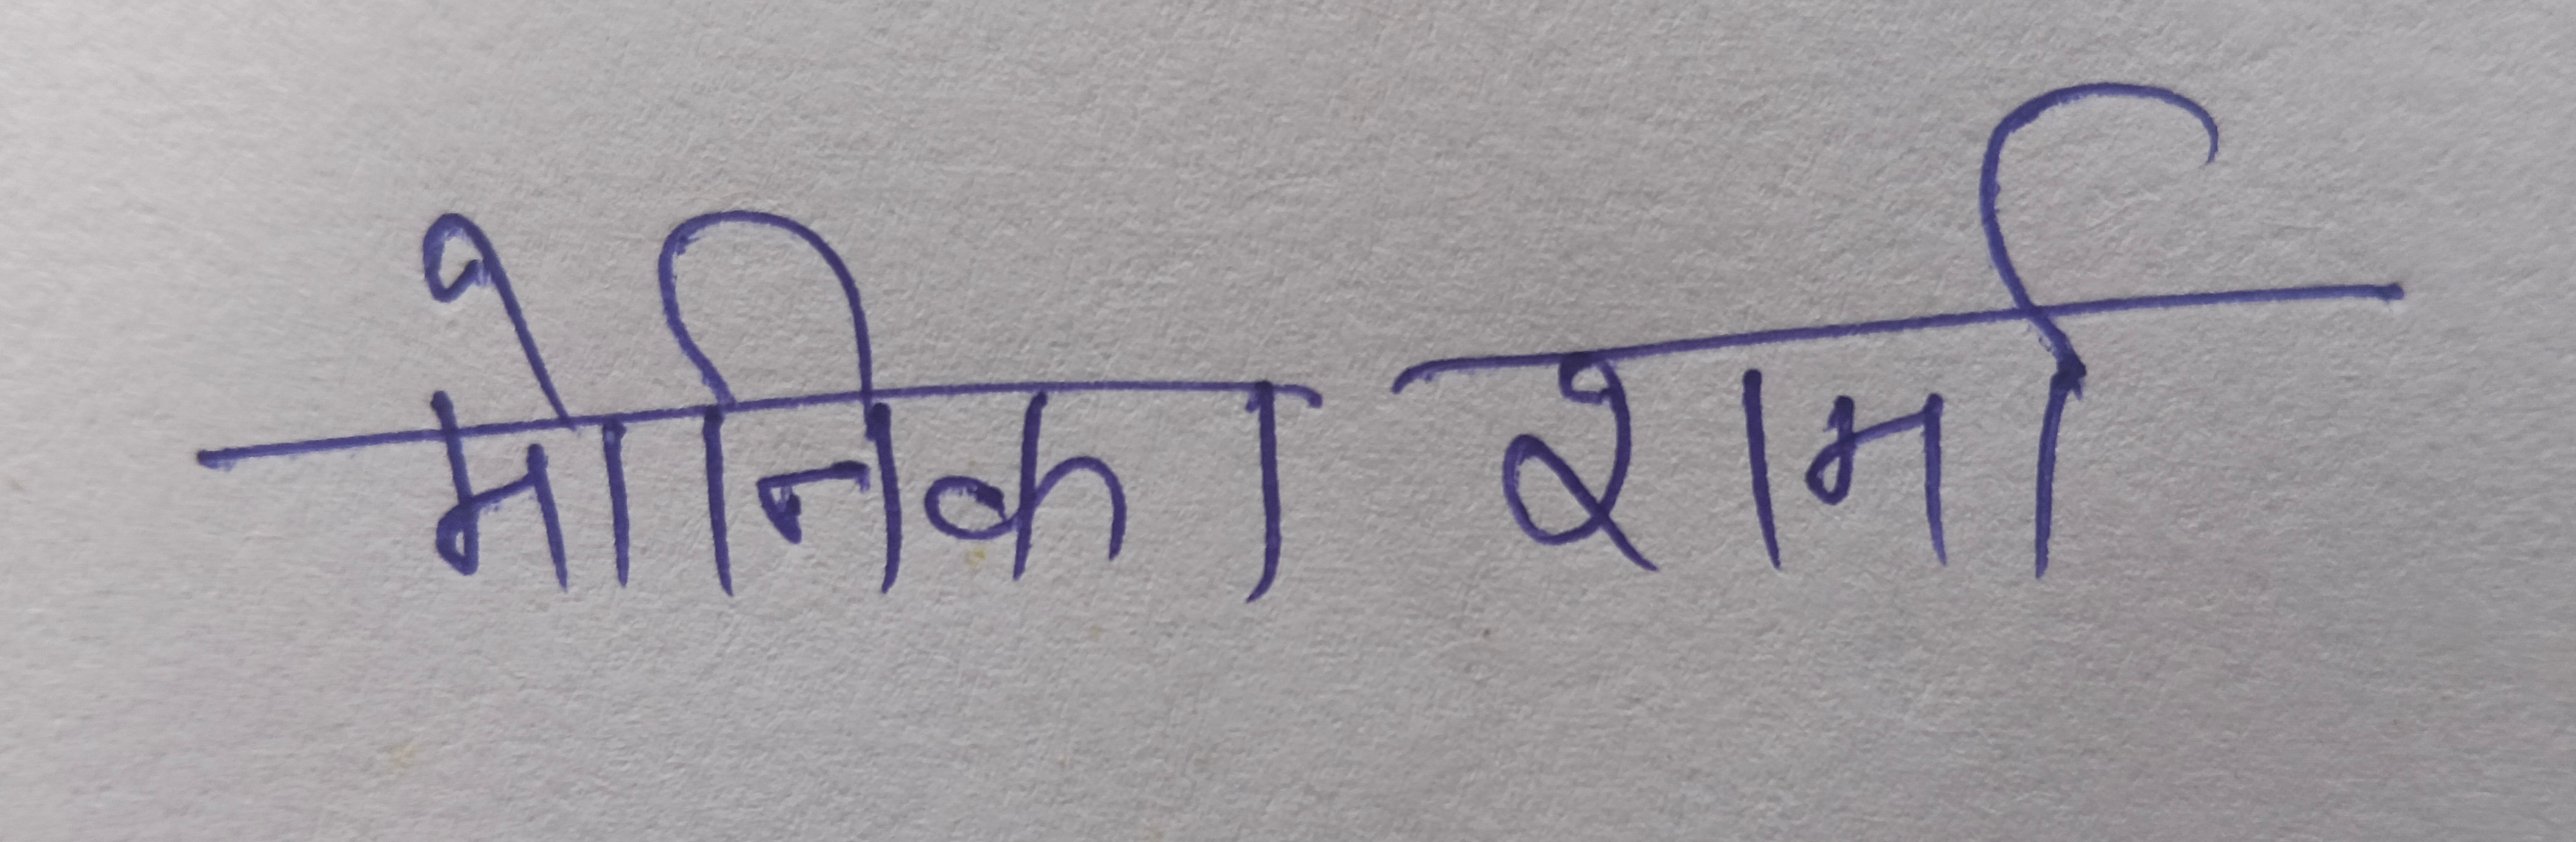
DPA signatory per Board Resolution
Dated: 25 October 2026 · Jhunjhunu, Rajasthan, India
CIN U62011RJ2026PTC119030 · Registered office: Khemi Sati Road, Jhunjhunu, Rajasthan – 333001 · legal@digitaliiisla.co.in